
How Opencomplai works
Opencomplai is an open-source, AGPL-3.0-licensed compliance engine that runs where your code already runs, not a dashboard you have to remember to check. Here is the mechanism, step by step.
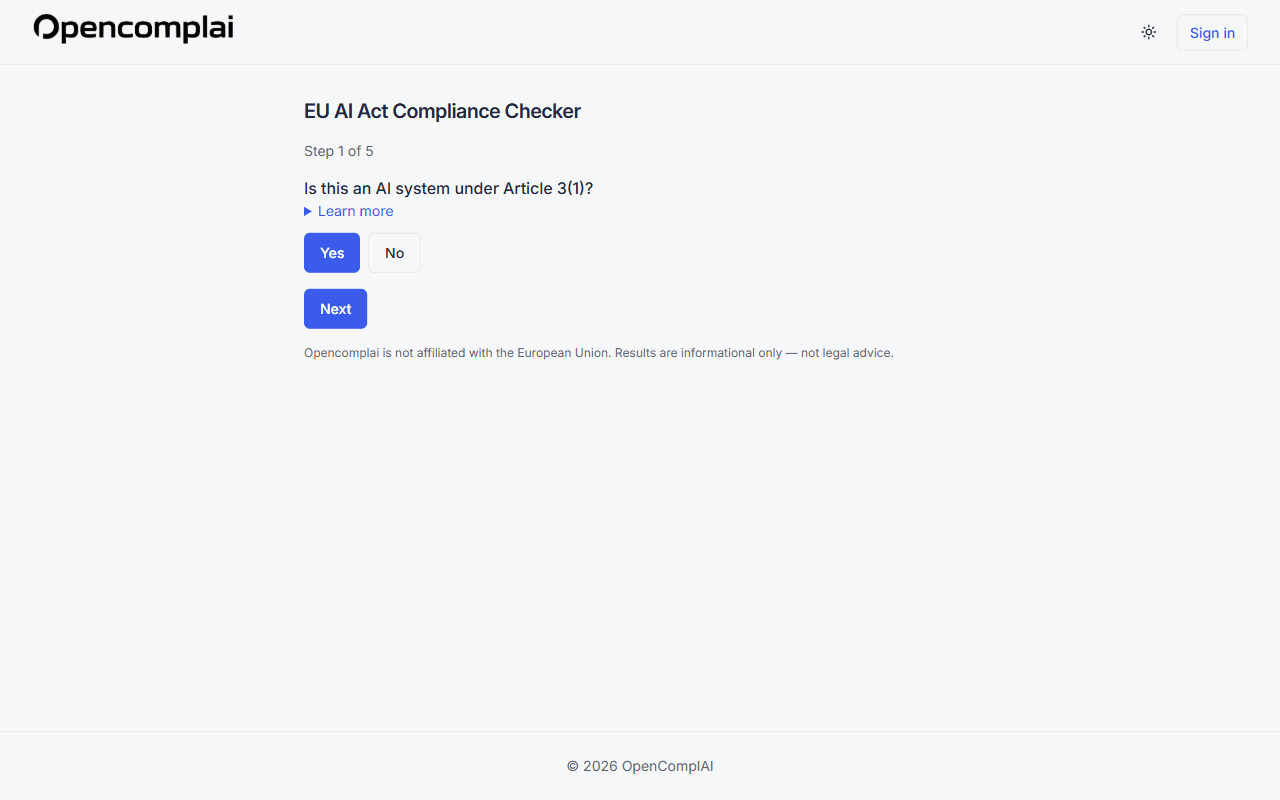
The EU AI Act applicability checker at app.opencomplai.com — no sign-in required.
1. Install
pip install opencomplai
A CLI and SDK you run in your own infrastructure. Nothing about your codebase leaves your environment during a normal scan.
2. Wire into CI/CD
Compliance checks on every commit
The GitHub Actions integration runs the same way a test suite does: on every commit and build. It flags high-risk classifications, missing audit trails, and transparency gaps before code ships.
3. Evidence, not paperwork
Automated audit readiness
Instead of writing manual documentation, OpenComplAI dynamically generates the legal mappings and evidence logs auditors ask for, tied to the actual state of your system at each build.
4. Ask when you're unsure
The Regulatory Oracle
A widget on our homepage that takes a plain-language question about your system and returns a classification answer, backed by the EU AI Act, NIST AI RMF, and ISO/IEC 42001. Useful for a quick gut check; don't paste confidential information into it.
Shadow AI, one source of truth
Because checks run in CI/CD rather than a separate portal, the model governance record stays a real-time reflection of what is actually deployed, not a spreadsheet someone updates quarterly. That is the gap this closes between engineering execution and legal oversight.
See it for yourself
The full source is on GitHub, and the packages are on PyPI. Read the code before you run it, that is the point of open source.